



CMMC phase II was just suspended. Here's what federal contractors still need to do.
On July 13, 2026, the Department of War (DoW) dropped a memo that sent a ripple of both relief and confusion through the Defense Industrial Base (DIB). CIO Kirsten Davies formally announced the immediate suspension of CMMC Phase II. For many, this felt like the finish line of a marathon had just been moved back ten miles, or perhaps disappeared entirely.
Share this blog on:


If you are a federal contractor, your first instinct might be to exhale, close your compliance spreadsheets, and put “CMMC” in the rearview mirror for a while.
I am here to tell you that would be a catastrophic mistake.
As someone who spends every day at H&V Complynt Cybersecurity Solutions thinking about the intersection of security and government mandate, I want to unpack the logic behind this pause. This isn’t a holiday from cybersecurity; it is a recalibration of the red tape. If you misunderstand the intent behind this memo, you risk your eligibility for future contracts and leave your organization exposed to the very threats the CMMC was designed to mitigate.
The logic of the pause: When the “Math Doesn’t Math”
To understand why the Department of War hit the brakes on Phase II, we have to look at the sheer scale of the DIB versus the capacity of the auditing industry
For the past two years, the Small Business Administration (SBA) and various industry advocacy groups have been sounding the alarm. The “math,” as they say, didn’t math. We have over 100,000 businesses in the DIB that would eventually require high-level certification, yet as of early 2026, we had barely 100 accredited third-party assessment organizations (C3PAOs) ready to conduct them.
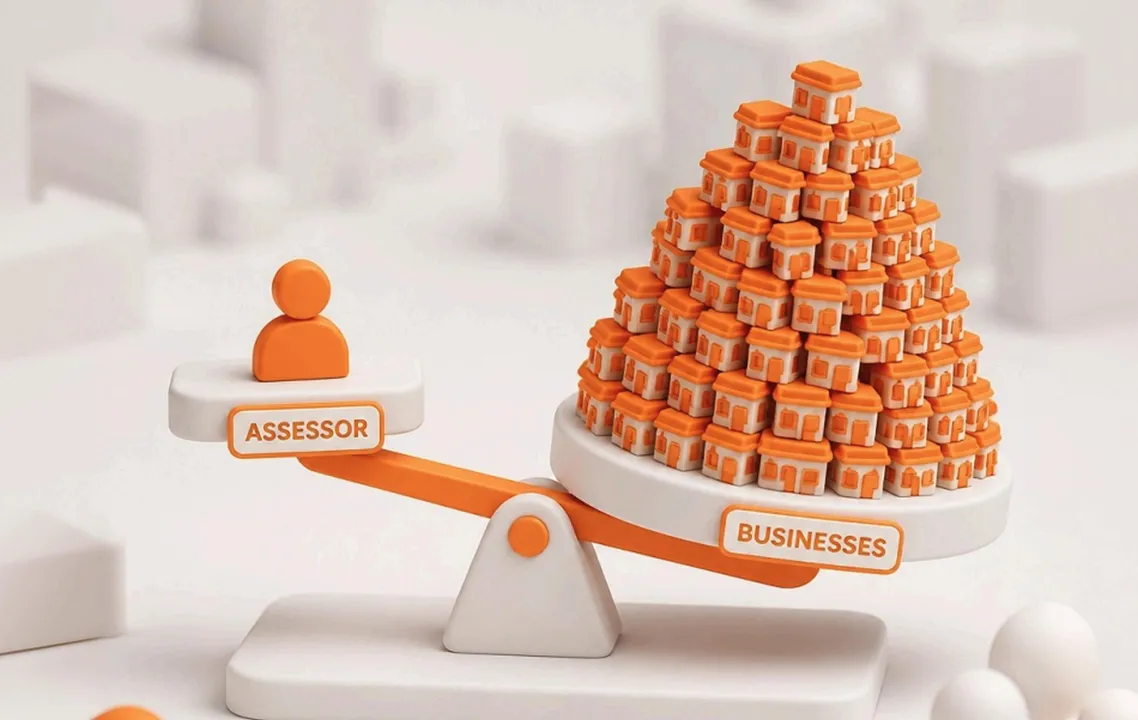
The bottleneck was not just a delay; it was a threat to “speed to capability.” The DoD cannot afford to lose 30% of its supply chain because those firms were stuck in an eighteen-month queue for an audit they couldn’t afford
Kirsten Davies’ memo and the formation of the CMMC Reform Task Force represent a moment of intellectual honesty from the Pentagon. They realize that administrative overhead cannot be allowed to throttle national security readiness. But: and this is the part many are missing: the suspension of the third-party audit is not a suspension of the security requirement.
The trap: Phase I is still mandatory
Here is the cold, hard reality: Phase I self-certification requirements remain in full effect.
If your contract calls for CMMC Level 1 (Self) or Level 2 (Self), nothing has changed. You are still legally obligated to:
- Conduct annual self-assessments.
- Maintain your System Security Plan (SSP).
- Manage your Plan of Action and Milestones (POA&Ms).
- Affirm your compliance in the Supplier Performance Risk System (SPRS).
In fact, one could argue that the stakes for self-certification have just gone up. Without a third-party auditor acting as a gatekeeper, the Department of War is placing a massive amount of trust in your executive affirmation. In a post-False Claims Act environment, an “affirmation” of security that isn’t backed by technical reality is a legal landmine.
At H&V Complynt, we often talk about the “map once, satisfy many” philosophy. Even with the Phase II pause, the underlying framework: NIST SP 800-171: remains the law of the land. If you handle Controlled Unclassified Information (CUI), you are still required to protect it. The DoW has merely paused the requirement for an external entity to verify your work. You are now the primary witness to your own security posture.
Understanding the 60-day review
The newly established CMMC Reform Task Force has 60 days to report back with “realistic, scalable security measures.” Their goal is to find a way to maintain high-grade security without the crippling costs that were projected for Phase II.
I suspect we will see a shift toward more automated, continuous monitoring and less emphasis on the “point-in-time” administrative audit. This aligns perfectly with our vision for compliance: security should be a lived reality, not a binder on a shelf.
The Task Force is looking for ways to leverage technology to bridge the gap. They want to see that you are actually doing the work, not just paying a consultant to help you pass a test. This “speed to capability” mindset means that those who have already automated their evidence collection and control mapping will be miles ahead when the new, streamlined requirements are announced in September.
My expert takeaway: Compliance isn’t paused, only the red tape
If you are a contractor, don’t stop your implementation. Use this 60-day window to get your house in order. The suspension of Phase II is a gift of time: time that should be spent strengthening your self-certification and ensuring your SPRS score is defensible.
We built the Complynt platform specifically for this hybrid world. Whether the government requires a third-party audit or a self-assessment, the evidence you need is the same. Our platform automates the heavy lifting of control mapping and evidence collection, allowing you to satisfy CMMC, NIST, and even SOC 2 requirements simultaneously.
You can see how we handle these complex facility and control system environments on our About page. We specialize in helping firms that operate in high-security environments (FedRAMP High, DoD IL5) navigate these exact types of regulatory pivots.
What You Should Do Today:
- Verify your current contract clauses: If you have DFARS 252.204-7012 or any CMMC “Self” requirements, you are still “on the clock.”
- Audit your SPRS score: Is your score based on actual implemented controls, or on a “wish list” of what you hope to do?
- Engage with the RFI: The Task Force is taking feedback until August 14. If the costs of Phase II were going to break your business, tell them.
- Automate your evidence: Don’t wait for an auditor to tell you what’s missing. Use a platform like Complynt to gain real-time visibility into your gaps.
The Department of War has acknowledged that the system was broken. That is a win for the industry. But don’t confuse a broken process with a broken mission. The mission remains the same: secure the DIB, or lose our competitive edge.
I, for one, am glad to see the focus return to actual security and “speed to capability.” Let’s use this pause to build something better.